PISB at the 13th National Forum on Critical Infrastructure Protection
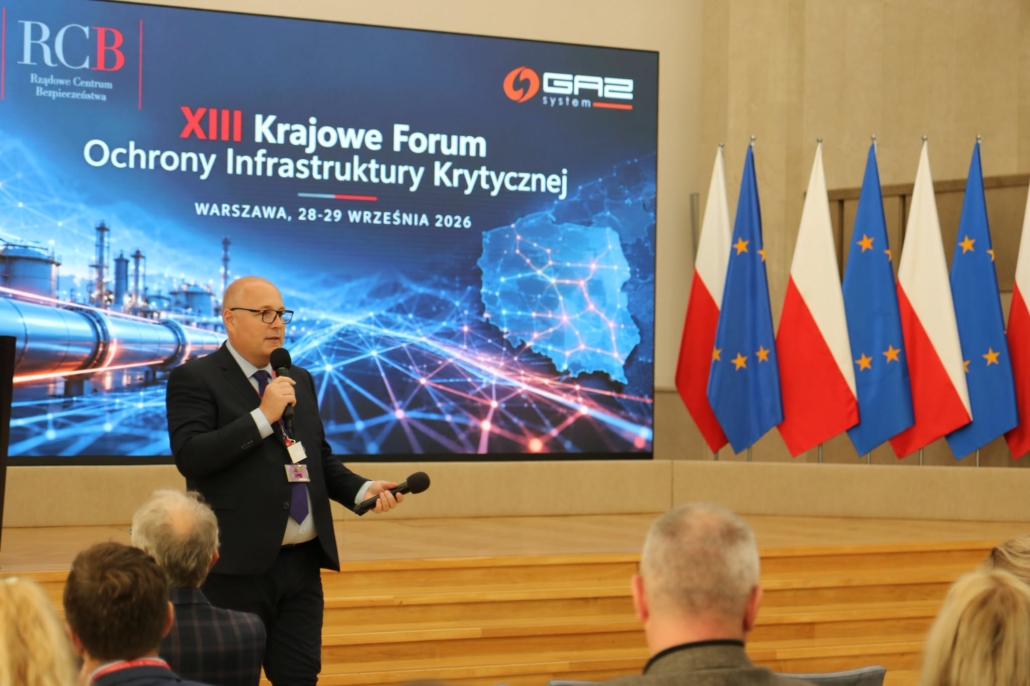
On 28 September 2026, the first day of the 13th National Forum on Critical Infrastructure Protection took place at the Chancellery of the Prime Minister, organised by the Government Centre for Security (RCB). The Polish Chamber of Unmanned Systems was represented by Aleksander Burwiel, Member of the Board.
The Forum was opened by Zbigniew Muszyński, Director of the Government Centre for Security, Wiesław Leśniakiewicz, Undersecretary of State at the Ministry of the Interior and Administration, and Konrad Frysztak, Member of Parliament and Deputy Chair of the Sejm Committee on Administration and Internal Affairs. The first day was devoted to the amendment of the Crisis Management Act as an element of building critical infrastructure resilience.
The Act of 29 May 2026 amending the Crisis Management Act and certain other acts (Journal of Laws 2026, item 815) has been in force since 4 July 2026 and implements Directive (EU) 2022/2557 on the resilience of critical entities. Below we set out two areas of particular relevance to the unmanned systems sector.
Counter-drone measures
The new provisions allow a critical infrastructure operator to decide independently on the use of telecommunications jamming devices by staff of specialised armed security formations. This requires prior notification of the devices’ parameters, and their operation must be limited to the minimum necessary time. It is not a general authorisation to neutralise any unmanned aircraft, but the possibility of applying a specific measure in response to a specific threat.
Destroying, disabling or taking control of an unmanned aircraft remains within the competence of the Police, Border Guard, State Protection Service and Military Police.
For suppliers, this means that counter-drone solutions sit within a broader process on the operator’s side: threat analysis, a decision-making procedure, preparation of security personnel and cooperation with the relevant services. The equipment is one element of that process.
Supply chain security
The Act introduces the concept of a critical supplier, meaning an entity providing products, technologies or services whose disruption could disrupt the functioning of critical infrastructure.
These obligations rest with the critical entity – a critical infrastructure operator entered into the register of critical entities. The critical entity identifies its critical suppliers, maintains a register of them, assesses them at least once a year, sets minimum security requirements for them and ensures contingency plans allowing such a supplier to be replaced.
The provisions also place obligations on critical suppliers themselves, including the reporting of significant incidents and submitting to audits carried out through the critical entity.
For technology companies working with this sector, this means requirements that go beyond the specifications of the product itself. They are worth understanding in advance – before they appear in a request for proposal or in a client’s procurement requirements.
A full account of the obligations and deadlines under the amendment is published by the Government Centre for Security.

Leave a Reply
Want to join the discussion?Feel free to contribute!